
Under the Cyber Resilience Act (CRA), cybersecurity will become a prerequisite for access to the EU market for many products with digital elements. But which products are affected? Which requirements do you need to meet? And where should you begin?
Our CRA Workbook helps you assess your current position, identify critical gaps in your products or processes, and prioritize the next steps.
Clarify CRA applicability and responsibilities
Systematically assess where action is needed
Turn 11 practical steps into a concrete implementation roadmap
Consider the EU Data Act from the outset
All CRA Requirements Will Apply From December 11, 2027
For equipment manufacturers and OEMs, the CRA is about more than security or documentation. Technical measures, development processes, vulnerability management, reporting processes, and proof of conformity must work together. Only then can you make affected products available on the EU market in compliance with the CRA.
Already in effect: Since September 11, 2026, the CRA reporting obligations have also applied to products that have already been delivered.
What the CRA Workbook Offers Equipment Manufacturers and OEMs
Identify Dead Ends
How to identify and overcome typical dead ends
Assess CRA Readiness
28 questions that reveal your current level of CRA readiness
Prioritize Implementation
11 practical steps lead to clear priorities and actions
Consider the EU Data Act
Identify overlaps and differences at an early stage
Which CRA Dead End Is Your Company Facing?
Many equipment manufacturers and OEMs have already started taking action. Yet implementation often stalls.
Regulations Are Considered in Isolation
Regulations Are Considered in Isolation
External Support Ends With Recommendations
External Support Ends With Recommendations
Ad Hoc Action Without Roadmap and Priorities
Ad Hoc Action Without Roadmap and Priorities
Compliance Is Treated Solely as a Cost Factor
Compliance Is Treated Solely as a Cost Factor
Turn Dead Ends Into Next Steps
Learn how to identify the four typical dead ends and why they will not get you to your goal. For each dead end, you will find a concrete way forward and a clear starting point for implementation.
28 Questions. Six Areas for Action. How Well Prepared Is Your Company for the CRA?
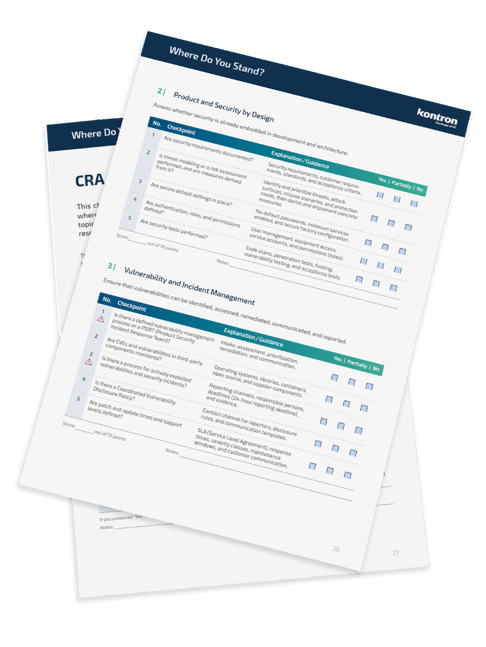
The CRA checklist systematically guides you through the areas that need to work together for successful CRA implementation:
CRA Scope
Product and Security by Design
Vulnerability and Incident Management
Lifecycle, Updates, and Device Management
SBOM, Supply Chain, and Documentation
Organization, Target State, and Implementation
The CRA checklist shows where you are already well positioned, where gaps remain, and which topics you should address first. This gives you a structured basis for setting priorities, clarifying responsibilities, and planning the next steps.
A Practical Perspective: From Single Issues to a Shared Roadmap
Manager Products & Digital Solutions, MackSmaTec GmbH
Richard Stegmann
At the outset, we were faced with numerous individual requirements related to the CRA and the EU Data Act. Each department focused on its own area, but we lacked a shared understanding of how hardware, software, data flows, and internal responsibilities interact. Once we brought all relevant departments together, we gained this overall picture for the first time. The many individual requirements became a clear roadmap that connects technical decisions, responsibilities, and priorities. This enabled us to turn regulatory requirements into tangible value for our customers.
Get Your Free CRA Workbook Now
FAQs About the CRA Workbook
Who is the CRA Workbook for?
The CRA Workbook is designed for equipment manufacturers and OEMs that develop, manufacture, or make products with digital elements available on the EU market. It particularly helps stakeholders in management, product development, service, and cybersecurity make an initial assessment of their CRA readiness.
Which products may be subject to the CRA?
The CRA may apply to hardware and software products that are made available on the EU market and are connected directly or indirectly to a device or network. These are referred to as products with digital elements. Examples include connected machines, controllers, gateways, operator interfaces, and embedded software. Whether a specific product falls within the scope of the CRA must be assessed on a case-by-case basis.
Is the CRA Workbook also relevant to equipment manufacturers and OEMs outside the EU?
Yes. What matters is not where the company is based, but whether an affected product is made available on the EU market. The CRA may therefore also apply to equipment manufacturers and OEMs outside the EU. The applicable obligations depend on the product and the company's role in the supply chain.
Does the CRA Workbook replace a legal or formal assessment?
No. As a guide with a checklist, the workbook provides structured orientation and helps you identify potential action needed for your products. It does not replace legal advice, an individual conformity assessment, or certification.